Compliance
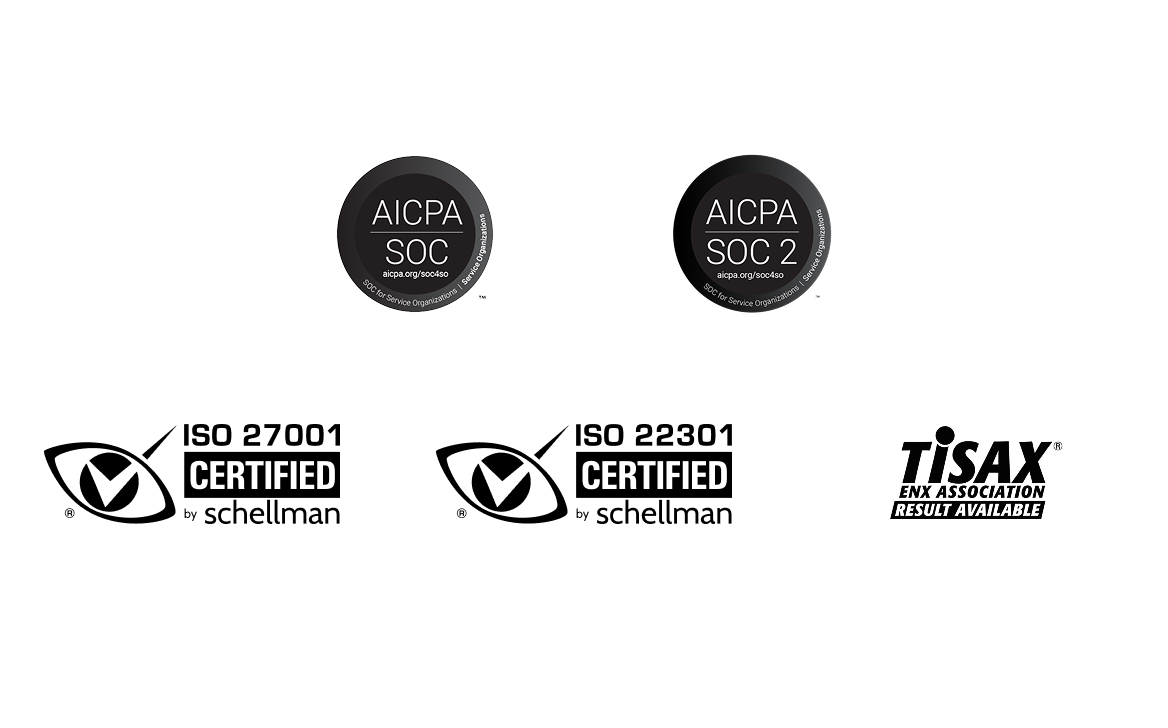
Compliance coverage across core products
Avalara’s most widely used products are individually attested under SOC 1 Type 2 and SOC 2 Type 2, certified to ISO 27001. Select products are also certified to ISO 22301 and assessed under TISAX.
What our assessments, attestations, and certifications cover
- SOC 1 Type 2
internal controls relevant to financial reporting
- SOC 2 Type 2
internal controls relevant to security
- ISO 27001
internationally recognized information security management
- ISO 22301
internationally recognized business continuity management
- TISAX
recognized information security assessment standard for the automotive industry
For a comprehensive list of product certifications, click Request compliance documents above.
Governance and oversight
- Aligned to the NIST Cybersecurity Framework (CSF) for risk management
- Governed by a formal compliance hierarchy, from executive policy to operational standards
See our Security section for the controls these certifications validate, and our Business Continuity and Disaster Recovery documentation for how our Business Continuity Management System (BCMS) is structured and tested.
Privacy and data regulation compliance
Our privacy program continuously supports and monitors GDPR (EU and UK), CCPA/CPRA (California), LGPD (Brazil), and other global frameworks. See Privacy for full principles, rights, and transfer mechanisms.
Security
Security protocols and controls
- Identity and access management
MFA and federated identity enforced across all production systems; no direct credential access permitted
- Endpoint security
continuous endpoint detection and response, feeding real-time telemetry into 24/7 security operations (SOC)
- Data protection
enterprise data loss prevention (DLP) on employee endpoints, and data-at-rest encryption for block stores and datastores for protection and confidentiality of customer data
- Network security
segmented networks with layered controls and continuous monitoring
- Vulnerability management
continuous external attack surface monitoring and remediation
- Independent testing and disclosure
annual third-party penetration testing on core products and APIs, supported by a Vulnerability Disclosure Program
- Application security
automated static (SAST), dynamic (DAST), and software composition analysis (SCA) with container scanning embedded in CI/CD pipelines, paired with security architecture reviews and threat modeling
- Secure cloud configuration
AWS, Azure, GCP, and OCI resources deployed against documented, continuously assessed security baselines
Monitoring and incident response
- 24/7 monitoring by Avalara’s dedicated SOC team
- Formal Security Incident Response process managed by Threat Detection and Response Team (TDR)
Vendor risk management
Vendors accessing Avalara or customer data sign DPAs/MSAs and undergo risk-based security review before onboarding, with ongoing monitoring by our Vendor Risk Management team.
Security awareness
All employees, contractors, and vendors with system access complete annual security training and biweekly phishing simulations.
Privacy
Privacy principles
- Lawfulness and transparency
lawful basis documented; notices clear
- Purpose limitation
data used only for stated purposes
- Data minimization
collection limited to what’s necessary
- Accuracy
data kept accurate and current
- Storage limitation
data retained by Avalara only as long as necessary
- Integrity and confidentiality
data protected by technical and organizational measures
- Accountability
compliance documented and demonstrable
Dedicated Data Protection Officer
Avalara has appointed a dedicated Data Protection Officer, supported by a global Privacy function, to oversee compliance with data protection laws worldwide and serve as a direct point of contact for privacy-related inquiries at dataprivacy@avalara.com.
Privacy and security by design and by default
The Privacy team, in close collaboration with Security, builds core principles into our products from the start. Least privilege access controls, data minimization, and purpose limitation are integrated into each stage of our software development life cycle.
Data subject rights
You may have the right to access, correct, delete, restrict, port, object to, or withdraw consent for the processing of your personal data. Submit requests via our privacy portal or email us at dataprivacy@avalara.com.
Data retention and deletion
We keep personal data only as long as needed for our services and legal obligations, then securely delete or anonymize it.
Privacy in AI-enabled features
The same privacy principles apply everywhere we use AI or automation. See AI Governance for how we govern responsible AI use.
International data transfers
Cross-border transfers are supported by EU SCCs, Brazil SCCs, the UK IDTA, and adequacy decisions where applicable, with Transfer Impact Assessments conducted as needed.
Data Processing Agreement
Our standard DPA is built into customer terms and covers data ownership, security obligations, incident notification, subprocessor management, and GDPR/CCPA compliance. It’s publicly available on our website; we don’t offer individualized DPAs given our scale (43,000+ customers globally).
Accountability and governance
Our program includes a Global Privacy Policy, RoPAs, DPIAs, LIAs, vendor due diligence, and mandatory annual training — overseen by our Privacy Legal team, led by our Principal Counsel for Privacy and AI.
Third-party and subprocessor management
Subprocessors undergo privacy and security due diligence and must meet or exceed our DPA standards, with ongoing risk-based monitoring. See our full list of subprocessors.
Security of personal data
Personal data is protected by the technical and organizational measures described in our Security section and DPA, with procedures to detect, contain, and notify in the event of an incident.
AI governance
Data processing
No.
Data is encrypted in transit and at rest, minimal data is cached in-browser, and AI follows Avalara’s identity and access controls.
Security controls and compliance
The core engine for Avalara AvaTax is deterministic and rule-based. For research questions, our AI uses Retrieval-Augmented Generation grounded in verified tax content.
Limitations and expectations
No. It recommends, you approve.
It flags the limitation, offers a manual fallback, and directs you to support; confidence scores are surfaced where relevant (e.g., product classification).
Infrastructure, availability, and integrations
Avalara retains AI interaction data for two years, then it’s automatically deleted; earlier deletion can be requested. This is separate from our third-party LLM providers that operate under Zero Data Retention (ZDR). They don’t retain your data for model training or store inference logs beyond what’s needed to return a response.
Yes. Avalara uses dedicated instance deployment through AI/LLM providers, such as Microsoft Azure, OpenAI, or private deployments, that are entirely Avalara-built and managed; customer data isn’t used to train our AI providers’ public or third-party models. All providers go through Avalara’s Vendor Risk review before onboarding, with ongoing monitoring by our Vendor Risk Management team. Our AI Center of Excellence (AI CoE) reviews and monitors all production models, including material changes.
Avalara AvaTax, Avalara Returns, Avalara Exemption Certificate Management, and Avalara Tax Research.
Avalara doesn’t use your proprietary or transaction data to train public models. Our AI is powered by a continuously updated global tax and trade content database (30,000+ jurisdictions, 190+ countries), and PII is masked/redacted in all data sent to LLMs — on top of standard transport security and access controls.
Business continuity and disaster recovery
Business Continuity Management System (BCMS)
- ISO 22301:2019-aligned; with BCMS alignment underway for key products
- Dedicated Business Continuity Management (BCM) office integrates continuity into everyday operations
- Plans tested and approved by senior leadership at least annually
Incident and crisis management
- Everyday incidents handled by Reliability, Product, IT, and Security Engineering teams
- Events escalate through a tiered structure — incident response and Crisis Management Teams (CMTs) manage isolated impacts with escalation to the Enterprise CMT for severe incidents
- Validated through annual CMT exercises and tabletop simulations
- After-Action Reports and Root Cause Analysis drive continuous improvement
Service reliability
- Deployment models matched to service criticality — from active-active multicloud (AWS, Azure, GCP, OCI) to single-AZ with in-place restore
- 24/7 monitoring, targeting 100% uptime outside published maintenance windows
- Global offices support coverage in case of regional disruptions
Sustainability
Environmental
Avalara is taking concrete steps to understand and reduce our environmental footprint.
- Climate risk is assessed in alignment with the Task Force on Climate-related Financial Disclosures (TCFD) framework.
- Supplier risk assessment program covers climate risk, labor practices, and GHG reporting.
Social
Avalara’s social impact starts with our people and extends through our products.
- Our workforce commitments support our winning culture and include Employee Resource Groups, continuous employee development, and full benefits that support employee well-being.
- Our products enable fair, accurate tax compliance for businesses worldwide, driving social impact in communities across the country.
Governance
Strong governance underpins every other ESG commitment.
- ESG policy approved by executive leadership and the Board
- Employee handbook, anti-bribery, and global trade compliance frameworks set consistent ethical standards